Cybersecurity & OS Foundations
The core principles of cybersecurity and operating system security.
You finish with
A hardened OS configuration and a security fundamentals report.
Cyber SecurityMost In-Demand
The incident response skillset Punjab's growing IT and financial sector is hiring for right now.
This bootcamp covers incident response through hands-on labs, live projects, and mentor-reviewed deliverables. You will build practical skills in threat detection, containment, eradication, and recovery, with dedicated placement support at the end.
Admissions open
Free demo class & counselling
Batch slots
Course overview
This Incident Response Bootcamp in Ludhiana is a structured programme covering incident response, from foundational threat detection through to containment, eradication, recovery, and digital forensics. The learning arc moves from foundations (SOC operations, threat detection) to applied work (incident response, AI in DFIR, digital forensics) to a capstone project where you execute a complete incident response simulation. Students finish with a portfolio of module deliverables, a documented internship certificate, and interview readiness for junior Incident Response Analyst and SOC Analyst roles in the local market.
Curriculum
The syllabus is structured as a ladder, not a set of parallel tracks. Each plan builds on the previous one, and longer plans repeat the full module list of shorter plans before adding their own advanced modules. This means you can start at the level that matches your experience and progress upward without gaps.
The core principles of cybersecurity and operating system security.
You finish with
A hardened OS configuration and a security fundamentals report.
How networks work and the core functions of a SOC.
You finish with
A working virtual SOC lab and a threat detection report.
Detecting and responding to security incidents.
You finish with
An incident response plan and a simulated investigation.
Investigating incidents using digital forensics.
You finish with
A forensic analysis report.
Analysing malware and using threat intelligence.
You finish with
A malware analysis report.
Automating security tasks and incident response.
You finish with
A security automation script for incident response.
Bringing together all incident response skills into a complete simulation.
You finish with
A complete incident response playbook and capstone report.
What you learn
The Incident Response Bootcamp in Ludhiana at techcadd is designed to help students move from basic cybersecurity concepts to practical, incident-response skills.
Understand the CIA triad, Windows and Linux permissions, and build a hardened OS configuration.
Work with OSI/TCP-IP, routing, DNS, and VPNs, and set up a SOC lab with SIEM and MITRE ATT&CK.
Operate Wazuh and Splunk, detect threats, and execute incident response workflows from containment to recovery.
Handle digital evidence properly, and perform memory and disk analysis using Autopsy and Volatility.
Perform static and dynamic malware analysis, use sandboxing, and map threats to IOC and STIX/TAXII.
Use Python and APIs to automate incident response tasks and report generation.
Execute a complete incident response simulation and apply AI-assisted DFIR techniques.
Tools you’ll work with
The objective is practical knowledge rather than memorised concepts — every module produces a portfolio-ready deliverable you can show to employers.
The case for it
A course is worth the time you give it only if you finish with work you can show and skills you can defend.
You learn incident response the way it is used in production, with the workflow and standards a SOC team expects.
You set up SIEM labs, investigate memory dumps, and analyse malware instead of just studying the theory.
You work with actual log data, forensic tools, and simulated breaches to solve problems you will face on the job.
Every module ends with a tangible project, giving you a professional incident response portfolio to show employers.
Why this course
Six things we hold ourselves to for every Incident Response Bootcamp batch that starts in Ludhiana.
Every module includes practical exercises on real SIEM tools and incident response scenarios, not simulations.
You work on live projects that mirror what incident response teams actually do, from alert triage to recovery reporting.
Every project is reviewed by mentors who still work on client engagements, not just teach.
Limited seats per batch ensure you get individual attention and feedback on your work.
Why TechCadd
What genuinely differs about this bootcamp at techcadd is that every module ends with a deliverable that goes into your portfolio, not a test score.
Your instructors are active security professionals, not full-time trainers, so you learn what the industry actually uses.
You work on real lab environments with real constraints, not simulations or case studies.
Limited seats mean you get individual feedback on every deliverable.
With campuses in Ludhiana, Mohali, Chandigarh, Phagwara, Hoshiarpur, Amritsar, and Jalandhar, techcadd has a local presence and a track record of over 10,000 students trained.
Who can join
This bootcamp fits anyone who wants to build a career in incident response but needs a structured path from fundamentals to job-ready skills.
You get a complete foundation in cybersecurity and incident response, starting with networking and SOC operations and progressing to full incident simulations.
You can upskill in DFIR, threat containment, and AI-assisted response through weekend batches, with deliverables that apply directly to your current work.
You start from the basics and build up to a capstone project, giving you a demonstrable skill set even if your background isn't in IT.
You learn to manage and respond to incidents in your own organisation, from detection to recovery.
Not sure which of these you are, or whether the timing works around what you already do? That is exactly what the call is for. Ask about Incident Response Bootcamp
Technology ecosystem
Incident Response Bootcamp is the centre. These are the tools you use around it in a working team.
Hands-on projects
Each one lands in your portfolio with the working files, the process and something a reviewer can open.
Certification
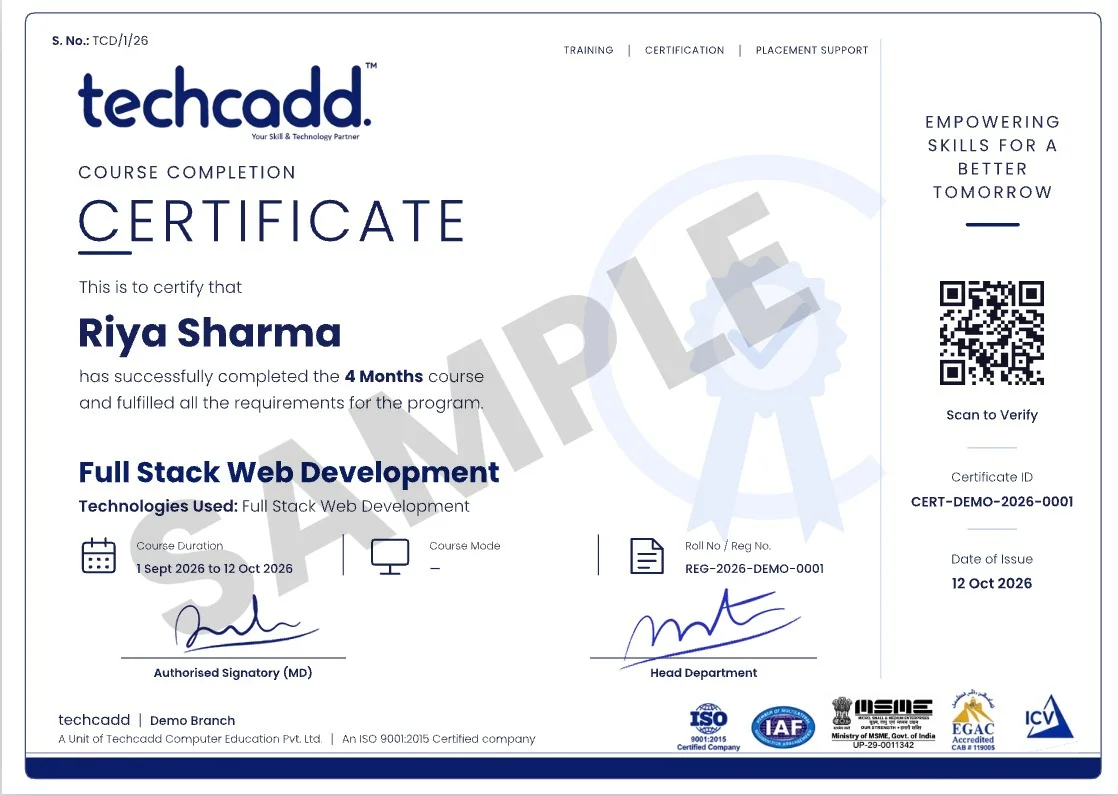
Finish the Incident Response Bootcamp programme at techcadd Ludhiana and you leave with more than a line on a CV — a verifiable certificate, and the project work that makes it mean something in an interview.
Issued in your name on completion of the Incident Response Bootcamp syllabus, with a reference number an employer can verify with us.
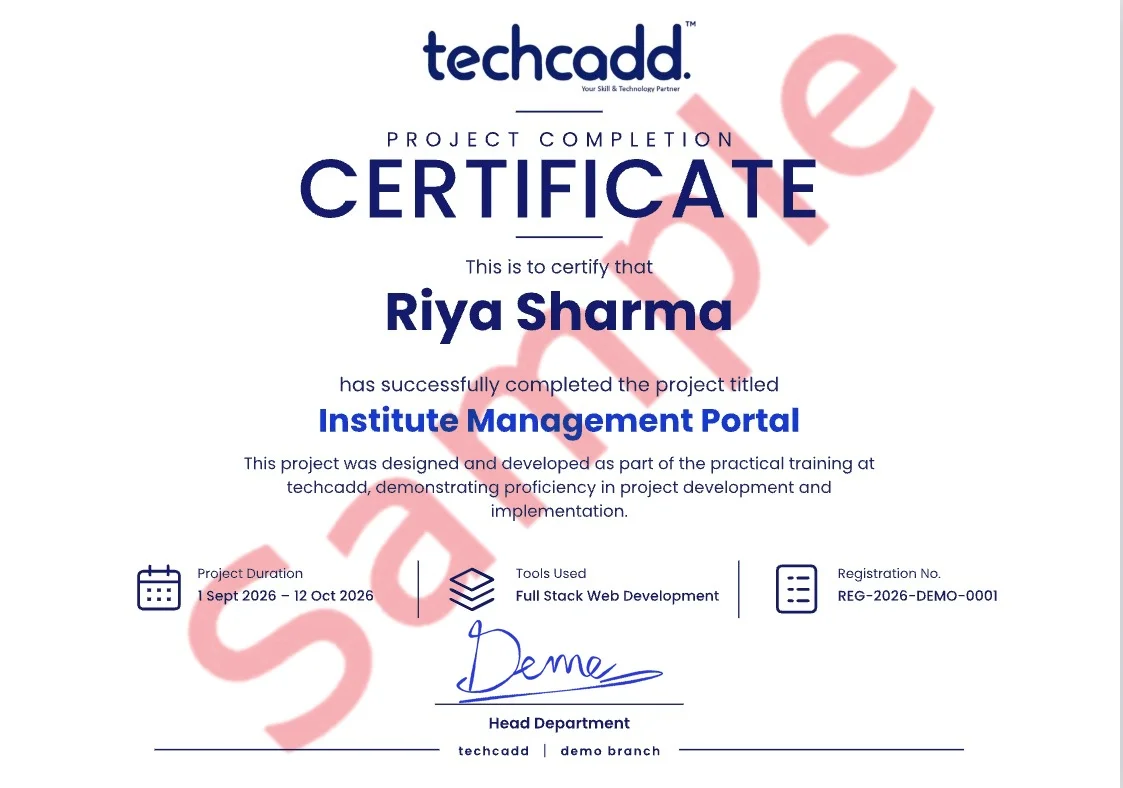
A separate certificate for the capstone you submit, naming the project so the work is attached to the credential.
Students who complete the live-project phase receive an internship letter covering the duration and the work delivered.
Every file, repository and deployed link stays yours — the part of the credential a reviewer can actually open.
techcadd has been training in Ludhiana since 2007. The certificate carries that record; the Incident Response Bootcamp work you did carries the rest.
Where it takes you
The route from your first module to the roles Incident Response Bootcamp opens — and the work that has to exist at each step.
Employers check your ability to investigate and document security incidents.
Employers check your ability to monitor alerts, triage incidents, and use SIEM tools.
Employers check your ability to perform digital forensics and malware analysis.
Employers check your ability to build detection rules using MITRE ATT&CK.
Salary outlook
Indicative ranges for the roles this course opens — what a fresher out of Ludhiana is offered, what the metro and remote markets pay for the same skills, and how that moves with two or three years of work behind you.
| Role | Ludhiana & Punjab | Delhi NCR & Bengaluru | Remote & freelance |
|---|---|---|---|
| Incident Response AnalystEntry | ₹2.4–4.2 LPA | ₹4–8 LPA | ₹20k–45k / project |
| SOC Analyst Entry to mid | ₹3.6–6.5 LPA | ₹6.5–14 LPA | ₹35k–90k / project |
| SOC Analyst Entry to mid | ₹3.6–6.5 LPA | ₹6.5–14 LPA | ₹35k–90k / project |
| Threat Detection AnalystMid | ₹3.6–6.5 LPA | ₹6.5–14 LPA | ₹35k–90k / project |
Ranges are indicative, drawn from what our own students report and from openings we see through the placement cell. Actual offers depend on your portfolio, the interview and the company — nobody can promise you a number, and we do not.
Incident Response Analyst, SOC Analyst , SOC Analyst , Threat Detection Analyst and related positions, depending on which part of the syllabus you go deepest on.
The first jump usually comes at 18–24 months, once you have shipped work you can point to. Depth in one area moves it faster than breadth across many.
Yes, and a good number of our students do. Remote and contract work is the reason Ludhiana candidates now compete for the same briefs as metro ones — the portfolio travels, the address does not matter.
IT services, manufacturing and export units running automation, e-commerce and D2C brands, healthcare, education, and the agencies serving all of them. Punjab hiring is broader than it looks from a job board.
It helps with the practical half. The projects and tooling carry into an M.Tech, MCA or a specialisation abroad, and the portfolio is often what separates two applicants with the same marks.
Future scope
A course ends; the field does not. Here is the honest version of what the next few years look like for Incident Response Bootcamp — where the roles go, and what is shifting underneath them while you learn.
Entry roles such as Incident Response Analyst open as soon as you have projects that run. At this stage nobody is asking about your marks — they are asking you to walk through something you built.
The generalists plateau; the specialists do not. Depth in one part of Incident Response Bootcamp — the part your first job leans on hardest — is what moves you towards soc analyst work.
Architecture, standards, hiring and mentoring. The technical skill is assumed by now; what you are paid for is judgement, and judgement only comes from having shipped things that mattered.
Teams expect Incident Response Bootcamp work to be done alongside AI tooling. It raises the floor on output and raises the bar on what counts as a junior — which is exactly why the fundamentals in this course are taught the hard way.
What used to be one narrow role now touches data, deployment and the product decision behind it. Every extra layer of Incident Response Bootcamp you understand is another kind of room you get invited into.
Remote and hybrid hiring means Ludhiana, Jalandhar and Chandigarh candidates now compete for the same roles as Bengaluru ones. Location has stopped being the ceiling it used to be.
Hiring has moved to portfolios, take-home tasks and live problem solving. A certificate opens a shortlist; work that runs is what gets you through the round after it.
Sectors hiring for this skill set
The comparison
This comparison covers the key differences between techcadd's Incident Response Bootcamp and typical alternatives.
| What to ask about | techcadd | Typical institute |
|---|---|---|
| Hands-on labs | Every module, from week one | Often only theory or limited labs |
| Batch size | Small, limited seats | Large, lecture-style batches |
| Mentor background | Active security professionals who do client work | Full-time trainers, often not current practitioners |
| Deliverables | Portfolio-ready projects every module | Tests and certificates |
Written about the market, not about any particular institute in it. Visit two or three, sit through a demo class at each, and ask all eight of these questions — that is the only version of this table worth trusting.
Student Voices
Feedback from students who completed the Incident Response Bootcamp programme at techcadd Ludhiana.
Simranjeet Kaur
Incident Response Bootcamp / B.Sc. IT graduate
I joined with no background in this. By the third month I was building Incident Response Bootcamp work on my own, and the project reviews are where I actually learnt to do it properly.
Harman Sethi
Incident Response Bootcamp / Now working as an intern in the field
The classes are practical. Every session ends with a task that has to work, so you cannot fake understanding. That habit helped me most in interviews.
Ankit Verma
Incident Response Bootcamp / BCA final year
Doubt support was the difference for me. My trainer sat with my work, found the mistake and made me fix it myself instead of handing over the answer.
Navjot Singh
Incident Response Bootcamp / Career switch from operations
I came for the skill and left with a portfolio — projects I could actually demo on a call, not a certificate I had to explain.
Real, unedited feedback from techcadd learners on Google.
Frequently asked questions
The 7 things people ask most often about the Incident Response Bootcamp course at techcadd Ludhiana.
The complete Incident Response Bootcamp programme runs for 3,6 or 9 months depending on the batch you choose. Weekday, weekend and fast-track options are available, along with shorter modules for students who only need the fundamentals.
School students after 12th, college students from any stream, graduates and working professionals changing track. The first module assumes no prior experience.
No. The course starts from the basics. If you already have some background, your trainer will move you faster through the first module so you reach the project work sooner.
Kali Linux, Ubuntu, Windows 10/11 , Wireshark, splunk, Wazuh, MTRE ATT&CK, Nmap, Python, Bash, VMare, Virtual Box, Git and Github — plus the day-to-day tooling and workflow that surrounds them in a real team.
Yes. Each module closes with a lab project, and the course ends with a capstone you can put on your portfolio and defend in an interview.
Placement support includes resume and portfolio review, aptitude and role-specific practice, mock interviews and interview referrals through our hiring network.
Yes. You receive a techcadd Incident Response Bootcamp completion certificate, and a separate project certificate for the capstone you submit.
Next batch
Send this form and a counsellor calls you back about this course specifically — batch dates, fees and whether it fits what you already know.
Would rather talk now? +91 98881 22667
Ready to get started?
Talk to a counsellor today. One call is usually enough to know which track fits your degree, your schedule and the job you want.
Call now+91 98881 22667