CybersecurityHigh Demand

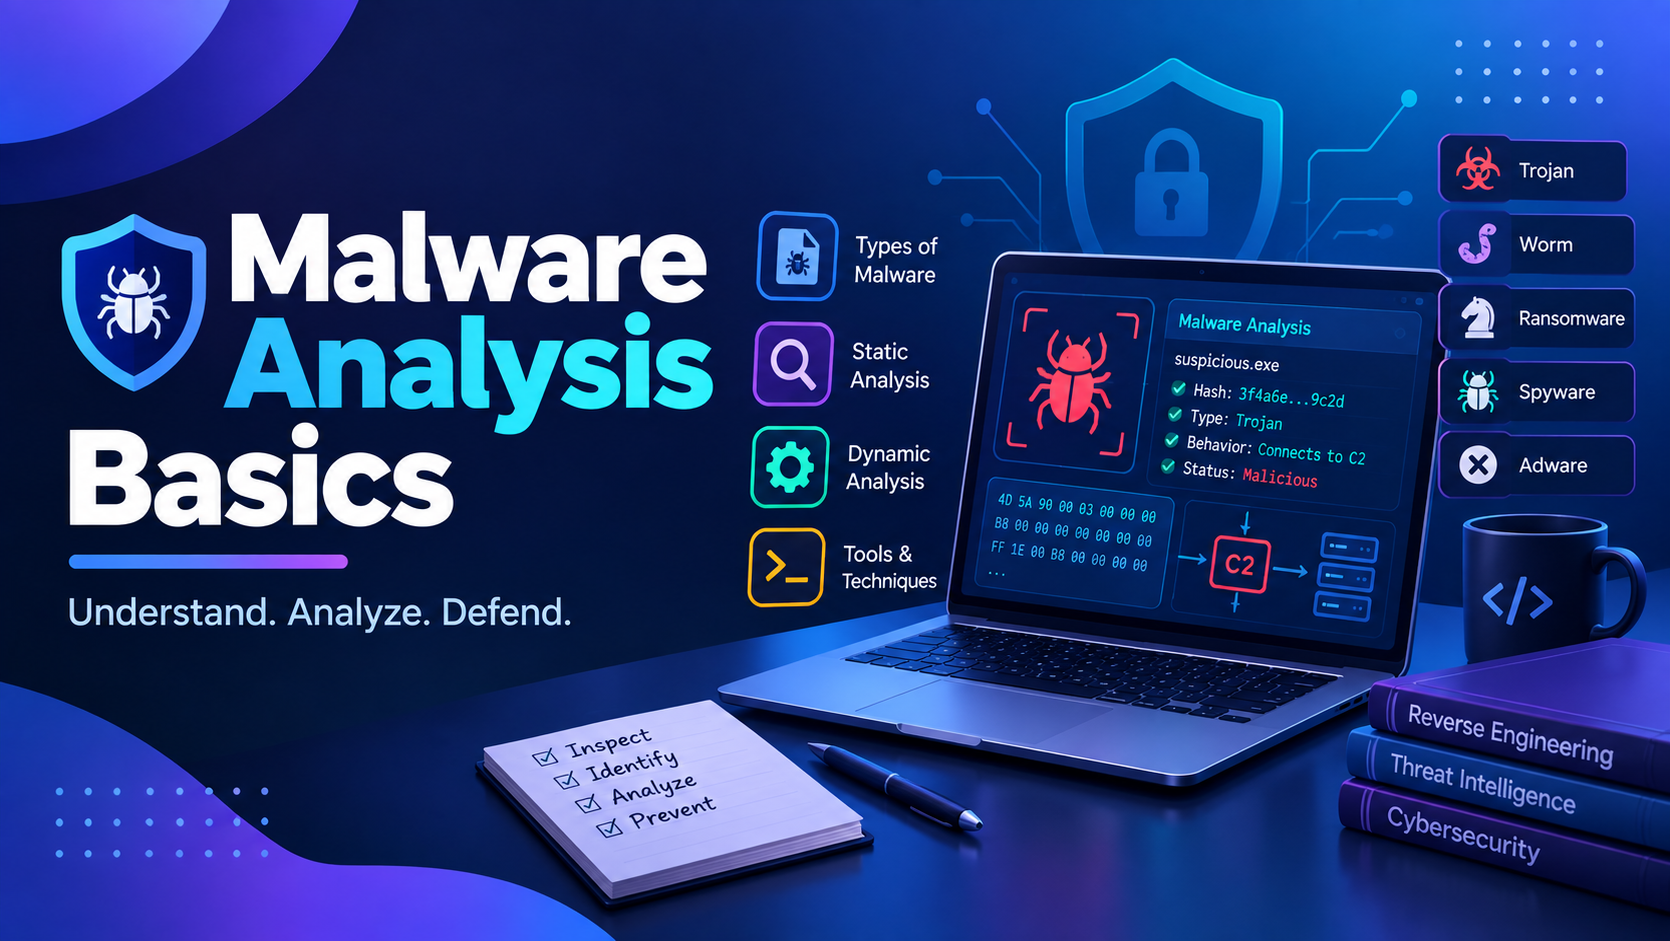
Malware Analysis Basics Course in Ludhiana with Live Labs & Placement Support

The skillset security operations centres in Punjab need to detect and stop threats before they spread.

This module is built for people who need to safely examine malicious files and understand what they do. You will work in isolated sandboxes, perform static and dynamic analysis, extract indicators of compromise (IOCs), and document your findings. Small batches, mentor-reviewed reports, and placement support are included.

 2 MonthsofflineBeginner to job ready
1.5 months
Duration
Weekday & weekend batches
Mode
Basic networking knowledge
Eligibility
techcadd Malware Analysis Certificate
Certification
Malware Analysis Basics

Course overview

Learn Malware Analysis Basics through practical experience

This is a 1.5-month Malware Analysis Basics Course in Ludhiana that teaches you to safely examine malicious files, not just define what malware is. The learning arc moves from malware fundamentals and static analysis, to dynamic analysis in a sandbox, and ends with threat intelligence and IOC reporting that a security team can use. You finish with a documented analysis report, a set of IOCs, a sandbox you configured, and interview readiness backed by techcadd’s placement support.

  • 2 Months programme
  • offline

Who can join

Who this Malware Analysis Basics course is for

This course fits anyone with basic networking knowledge who wants to work directly on threat detection and incident response.

  • SOC Analysts (Entry-Level)

    You already monitor alerts but need to understand what a suspicious file actually does. You will learn to triage malware and write IOC reports.

  • IT Security Administrators

    You manage endpoints and need to respond to infections. You will learn to isolate and analyse a sample safely before deciding on containment.

  • Cybersecurity Students

    You have theoretical knowledge but no hands-on lab experience. This course gives you a real sandbox workflow and a report to show employers.

  • Incident Responders

    You need to move faster during an outbreak. You will learn static and dynamic techniques to identify malware family and behaviour quickly.

What you actually need before day one

2 Months · offline

  • A laptop or desktop — we help you set it up in the first session
  • A stable internet connection for the online batches
  • No prior coding or technical background
  • Basic English reading — the tools and their documentation are in English
  • About 6-8 hours a week outside class for practice
  • Willingness to finish the lab task before the next class

Not sure which of these you are, or whether the timing works around what you already do? That is exactly what the call is for. Ask about Malware Analysis Basics

The case for it

Your months should build more than a certificate.

A course is worth the time you give it only if you finish with work you can show and skills you can defend. This programme is built in a live isolated sandbox, so you configure a VM, run static and dynamic analysis on real samples, and write an IOC report yourself, and every deliverable is reviewed by a mentor who still works on incident response.

3Practical learning areasfrom static analysis to IOC reporting
  • You are not watching slides; you are configuring a VM and safely running real malware samples in a contained environment.

  • Each module ends with a specific deliverable — a static analysis, a dynamic behaviour log, an IOC report — that a mentor checks line-by-line for accuracy and completeness.

  • You learn to examine a file without running it, then observe its real behaviour with Procmon and Wireshark, and tie both into a single investigation.

  • You finish with a documented IOC report, a sandbox you configured, a verified internship certificate, and interview readiness backed by techcadd's placement support.

What you will learn

A path from first steps to shipped work

The syllabus is structured as a ladder, not a set of parallel topics. You start with malware fundamentals and static analysis, then move to dynamic analysis in a sandbox, and finish with threat intelligence and reporting.

3 learning modules01 / 03
Module 01

Malware Fundamentals & Static Analysis

This module introduces malware families and teaches you to examine a file without running it.

Skills you build

    Tools & libraries

      You finish with

      A static analysis report with file properties and embedded strings.

      Every module includes hands-on practice in a live isolated lab or on a real deliverable, not a slide demonstration.

      What you learn

      What you will learn in the Malware Analysis Basics course

      The Malware Analysis Basics Course in Ludhiana at techcadd is designed to help students move from basic security concepts to practical malware investigation and reporting.

      • 01

        Set up a safe malware analysis lab

        You will configure an isolated VM and sandbox environment, so you can run suspicious samples without risking the host machine or network.

      • 02

        Perform static analysis on a suspicious file

        You will examine file properties, extract embedded strings, and use tools like PEiD and VirusTotal to identify potential malware family and behaviour without running the file.

      • 03

        Perform dynamic analysis in a sandbox

        You will run a sample safely and observe process, file, and network activity with Procmon and Wireshark, logging every action it takes.

      • 04

        Extract indicators of compromise

        You will pull file hashes, IP addresses, domains, and registry keys from the analysis, and structure them for use in a SOC workflow.

      • 05

        Write a threat intelligence report

        You will document your findings in a clear IOC report that a security team could act on, using threat intelligence frameworks like TTP, STIX, and TAXII.

      • 06

        Present a malware investigation

        You will walk through your analysis and defend your conclusions, simulating a real SOC handoff and building interview confidence.

      Tools you’ll work with

      • VMware
      • VirtualBox
      • Kali Linux
      • Windows 10/11
      • Procmon
      • Wireshark
      • PEiD
      • Strings
      • VirusTotal
      • Any.Run
      • Wazuh

      The objective is practical investigation skill rather than memorised definitions.

      Technology ecosystem

      One discipline.
      A mesh of real tools.

      Malware Analysis Basics is the centre. These are the tools you use around it in a working team.

      • Virtualization
      • Security OS
      • Operating system
      • System monitoring
      • Network analysis
      • Static analysis
      • Static analysis
      • Threat intelligence
      • Sandbox
      • SIEM
      • VMware / VirtualBoxVirtualization
      • Kali LinuxSecurity OS
      • Windows 10/11Operating system
      • ProcmonSystem monitoring
      • WiresharkNetwork analysis
      • PEiDStatic analysis
      • stringsStatic analysis
      • VirusTotalThreat intelligence
      • Any.RunSandbox
      • WazuhSIEM

      Hands-on projects

      Projects you actually ship,
      not just follow along with.

      Each one lands in your portfolio with the working files, the process and something a reviewer can open.

      Certification

      Get certified in Malware Analysis Basics

      Finish the Malware Analysis Basics programme at techcadd Ludhiana and you leave with more than a line on a CV — a verifiable certificate, and the project work that makes it mean something in an interview.

      • Course completion certificate

        Issued in your name on completion of the Malware Analysis Basics syllabus, with a reference number an employer can verify with us.

      • Project certificate

        A separate certificate for the capstone you submit, naming the project so the work is attached to the credential.

      • Internship letter

        Students who complete the live-project phase receive an internship letter covering the duration and the work delivered.

      • Portfolio you own

        Every file, repository and deployed link stays yours — the part of the credential a reviewer can actually open.

      techcadd has been training in Ludhiana since 2007. The certificate carries that record; the Malware Analysis Basics work you did carries the rest.

      Course completion

      This is to certify that

      has successfully completed the Malware Analysis Basics programme

      Malware Analysis Basics

      Ref TC-XXXX-XXXX
      Project & internship

      This is to certify that

      for project work delivered under supervision in Ludhiana

      Malware Analysis Basics capstone

      Ref TC-PRJ-XXXX

      Where it takes you

      Where this course takes you

      The route from your first module to the roles Malware Analysis Basics opens — and the work that has to exist at each step.

      1. 01Learning
      2. 02Projects
      3. 03Portfolio
      4. 04Industry readiness
      5. 05Career opportunities
      • SOC Analyst

        An employer checks if you can triage a suspicious file, extract IOCs, and write a report — all of which are module deliverables.

      • Malware Analyst

        The role tests your ability to perform static and dynamic analysis safely; your sandbox project and report are direct proof of this skill.

      • Incident Responder

        Employers look for experience with containment and IOC extraction; your analysis workflow demonstrates this.

      • IT Security Administrator

        The job checks your ability to identify and respond to malware on endpoints; your dynamic analysis is the proof.

      Salary outlook

      What Malware Analysis Basics pays, and where

      Indicative ranges for the roles this course opens — what a fresher out of Ludhiana is offered, what the metro and remote markets pay for the same skills, and how that moves with two or three years of work behind you.

      Indicative annual packages by role and market
      RoleLudhiana & PunjabDelhi NCR & BengaluruRemote & freelance
      SOC AnalystEntry₹2.4–4.2 LPA₹4–8 LPA₹20k–45k / project
      Malware Analyst Entry to mid₹3.6–6.5 LPA₹6.5–14 LPA₹35k–90k / project
      Incident ResponderEntry to mid₹3.6–6.5 LPA₹6.5–14 LPA₹35k–90k / project
      IT Security AdministratorMid₹3.6–6.5 LPA₹6.5–14 LPA₹35k–90k / project

      Ranges are indicative, drawn from what our own students report and from openings we see through the placement cell. Actual offers depend on your portfolio, the interview and the company — nobody can promise you a number, and we do not.

      • SOC Analyst, Malware Analyst , Incident Responder, IT Security Administrator and related positions, depending on which part of the syllabus you go deepest on.

      • The first jump usually comes at 18–24 months, once you have shipped work you can point to. Depth in one area moves it faster than breadth across many.

      • Yes, and a good number of our students do. Remote and contract work is the reason Ludhiana candidates now compete for the same briefs as metro ones — the portfolio travels, the address does not matter.

      • IT services, manufacturing and export units running automation, e-commerce and D2C brands, healthcare, education, and the agencies serving all of them. Punjab hiring is broader than it looks from a job board.

      • It helps with the practical half. The projects and tooling carry into an M.Tech, MCA or a specialisation abroad, and the portfolio is often what separates two applicants with the same marks.

      Next batch

      Enquire about Malware Analysis Basics

      Send this form and a counsellor calls you back about this course specifically — batch dates, fees and whether it fits what you already know.

      • CourseMalware Analysis Basics
      • Duration2 Months
      • Modeoffline
      • Centretechcadd Ludhiana

      Would rather talk now? +91 98881 22667

      Taken from the page you are on — this enquiry reaches the Malware Analysis Basics counsellor directly.

      Loading the security check…

      We never share your number. Expect a call within working hours.

      Frequently asked questions

      Questions before you enrol

      The 7 things people ask most often about the Malware Analysis Basics course at techcadd Ludhiana.

      • The complete Malware Analysis Basics programme runs for 2 Months depending on the batch you choose. Weekday, weekend and fast-track options are available, along with shorter modules for students who only need the fundamentals.

      • School students after 12th, college students from any stream, graduates and working professionals changing track. The first module assumes no prior experience.

      • No. The course starts from the basics. If you already have some background, your trainer will move you faster through the first module so you reach the project work sooner.

      • VMware / VirtualBox, Kali Linux, Windows 10/11, Procmon, Wireshark, PEiD, strings, VirusTotal, Any.Run and Wazuh — plus the day-to-day tooling and workflow that surrounds them in a real team.

      • Yes. Each module closes with a lab project, and the course ends with a capstone you can put on your portfolio and defend in an interview.

      • Placement support includes resume and portfolio review, aptitude and role-specific practice, mock interviews and interview referrals through our hiring network.

      • Yes. You receive a techcadd Malware Analysis Basics completion certificate, and a separate project certificate for the capstone you submit.

      Why this course

      Why should you choose this course?

      Six things we hold ourselves to for every Malware Analysis Basics batch that starts in Ludhiana.

      • 01

        Live Isolated Lab:

        You work in a safe sandbox environment from the first module, not a simulation.

      • 02

        Mentor-Reviewed Reports

        Every deliverable — a static analysis, a dynamic behaviour log, an IOC report — is reviewed by a mentor who works on incident response.

      • 03

        Real IOC Extraction

        You build a set of indicators of compromise (file hashes, network IOCs, registry keys) that you can use in a real SOC workflow.

      Why TechCadd

      Why students choose us for this

      At techcadd, this course is taught in a live isolated lab with mentor-reviewed reports, so you finish with a portfolio an employer can verify, not just a certificate.

      • Mentors Who Work on Incident Response

        Your instructors are actively responding to security incidents, so they teach current malware behaviour, not textbook theory.

      • Live Sandbox, Not Simulations

        You configure and use a real isolated environment from the first module. You learn to handle real samples safely.

      • Small Batch Sizes

        Batches are capped so the mentor can review every student’s analysis and troubleshoot issues individually.

      • ISO 9001:2015 Certified Institute

        techcadd is an ISO-certified training institute with 10,000+ students trained and 100+ career courses delivered.

      Future scope

      The road ahead for Malware Analysis Basics

      A course ends; the field does not. Here is the honest version of what the next few years look like for Malware Analysis Basics — where the roles go, and what is shifting underneath them while you learn.

      1. Year 0–1

        Get in on proof of work

        Entry roles such as SOC Analyst open as soon as you have projects that run. At this stage nobody is asking about your marks — they are asking you to walk through something you built.

      2. Year 2–4

        Specialise and get paid for it

        The generalists plateau; the specialists do not. Depth in one part of Malware Analysis Basics — the part your first job leans on hardest — is what moves you towards malware analyst work.

      3. Year 5+

        Own the decisions

        Architecture, standards, hiring and mentoring. The technical skill is assumed by now; what you are paid for is judgement, and judgement only comes from having shipped things that mattered.

      Sectors hiring for this skill set

      • IT services
      • Product startups
      • Banking & fintech
      • Healthcare
      • E-commerce
      • Manufacturing
      • EdTech
      • Government & PSUs

      The comparison

      Why students pick techcadd for Malware Analysis Basics

      This comparison covers how techcadd’s malware analysis training differs from a typical institute course.

      techcadd compared with a typical institute, feature by feature
      What to ask abouttechcaddTypical institute
      Live LabEvery student configures and uses an isolated sandbox from module one.Often taught via slides or pre-recorded demos only.
      Mentor ReviewEvery analysis report is reviewed line-by-line by a mentor.Feedback is often limited to a final exam score.
      Course FocusBuilt around analysing real samples safely.Often focused on passing a certification exam.
      Batch SizeCapped to ensure individual troubleshooting time.Can be large, lecture-style batches.
      CertificateDocumented internship certificate with hours and projects.A course completion certificate with no project detail.

      Every comparison here is about substance, not marketing language.

      Student Voices

      What Malware Analysis Basics learners say

      Feedback from students who completed the Malware Analysis Basics programme at techcadd Ludhiana.

      Google Reviews4.8from 181 Google reviewsGoogle Verified
      SK

      Simranjeet Kaur

      Malware Analysis Basics / B.Sc. IT graduate

      I joined with no background in this. By the third month I was building Malware Analysis Basics work on my own, and the project reviews are where I actually learnt to do it properly.

      Posted on Google
      HS

      Harman Sethi

      Malware Analysis Basics / Now working as an intern in the field

      The classes are practical. Every session ends with a task that has to work, so you cannot fake understanding. That habit helped me most in interviews.

      Posted on Google
      AV

      Ankit Verma

      Malware Analysis Basics / BCA final year

      Doubt support was the difference for me. My trainer sat with my work, found the mistake and made me fix it myself instead of handing over the answer.

      Posted on Google
      NS

      Navjot Singh

      Malware Analysis Basics / Career switch from operations

      I came for the skill and left with a portfolio — projects I could actually demo on a call, not a certificate I had to explain.

      Posted on Google
      SK

      Simranjeet Kaur

      Malware Analysis Basics / B.Sc. IT graduate

      I joined with no background in this. By the third month I was building Malware Analysis Basics work on my own, and the project reviews are where I actually learnt to do it properly.

      Posted on Google
      HS

      Harman Sethi

      Malware Analysis Basics / Now working as an intern in the field

      The classes are practical. Every session ends with a task that has to work, so you cannot fake understanding. That habit helped me most in interviews.

      Posted on Google
      AV

      Ankit Verma

      Malware Analysis Basics / BCA final year

      Doubt support was the difference for me. My trainer sat with my work, found the mistake and made me fix it myself instead of handing over the answer.

      Posted on Google
      NS

      Navjot Singh

      Malware Analysis Basics / Career switch from operations

      I came for the skill and left with a portfolio — projects I could actually demo on a call, not a certificate I had to explain.

      Posted on Google
      SK

      Simranjeet Kaur

      Malware Analysis Basics / B.Sc. IT graduate

      I joined with no background in this. By the third month I was building Malware Analysis Basics work on my own, and the project reviews are where I actually learnt to do it properly.

      Posted on Google
      HS

      Harman Sethi

      Malware Analysis Basics / Now working as an intern in the field

      The classes are practical. Every session ends with a task that has to work, so you cannot fake understanding. That habit helped me most in interviews.

      Posted on Google
      AV

      Ankit Verma

      Malware Analysis Basics / BCA final year

      Doubt support was the difference for me. My trainer sat with my work, found the mistake and made me fix it myself instead of handing over the answer.

      Posted on Google
      NS

      Navjot Singh

      Malware Analysis Basics / Career switch from operations

      I came for the skill and left with a portfolio — projects I could actually demo on a call, not a certificate I had to explain.

      Posted on Google

      Real, unedited feedback from techcadd learners on Google.

      Ready to get started?

      Start building your career today.

      Talk to a counsellor today. One call is usually enough to know which track fits your degree, your schedule and the job you want.

      Call now+91 98881 22667
      • Free career counselling
      • No registration fee
      • Placement support included